Cybersecurity & NIS2 Compliance
We secure software ecosystems, conduct penetration testing, and implement NIS2 compliance frameworks to protect critical IT infrastructure against cyber threats.
NIS2 Directive, Audits & Threat Protection
Cybersecurity - Digital Confidence
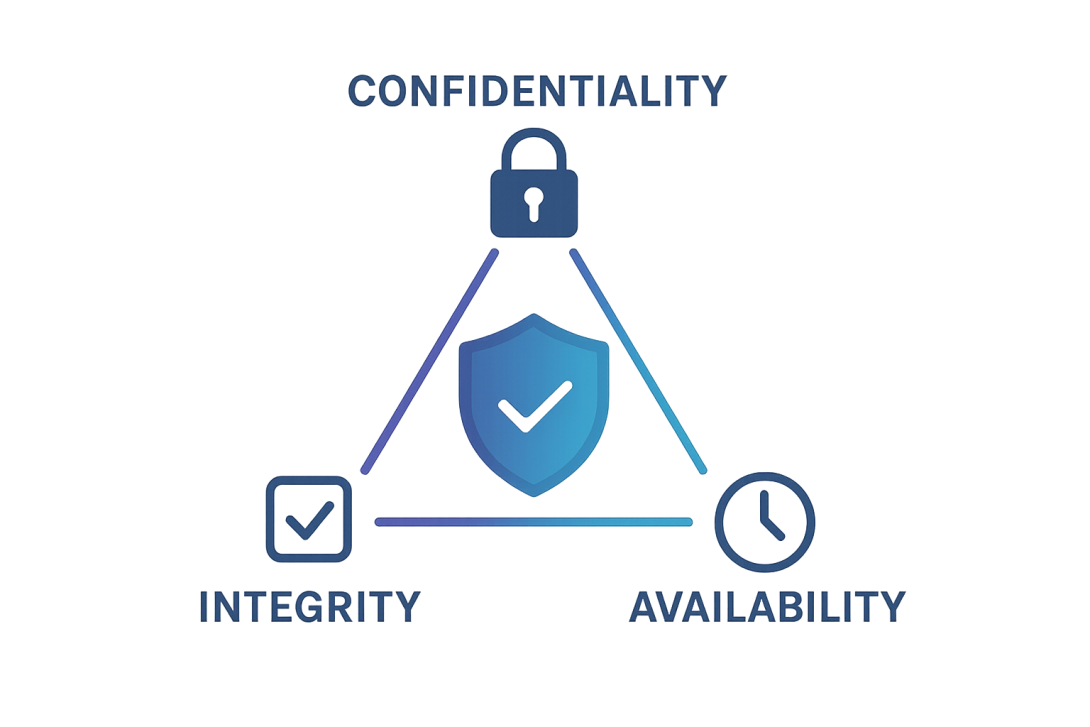
It includes the so-called CIA Triad (Confidentiality, Integrity, Availability), which refers to measures aimed at ensuring:
- confidentiality (access only for authorized users),
- integrity (no unauthorized modifications),
- availability of data and services.
Main areas of cybersecurity:
- Network security – protecting IT infrastructure against intrusions and attacks (firewalls, IDS/IPS, VPN),
- Application security – eliminating software vulnerabilities (penetration testing, SAST/DAST),
- Data security – encryption, access control, backup policies,
- User security (security awareness) – education on phishing and social engineering,
- Endpoint protection – antivirus, EDR, patch management,
- Incident Response – detection, analysis, and mitigation of attack consequences,
- Identity and Access Management (IAM) – controlling who has access to what,
- Regulatory compliance – meeting legal requirements (GDPR, NIS Directive, ISO 27001)
Why is it important?
Cybercriminals may attack to steal data, demand ransom (ransomware), sabotage, spy, or simply create chaos. Cybersecurity minimizes these risks and enables companies, institutions, and individuals to use technology safely.
Cybersecurity is crucial for any organization because, without it, all other processes and resources can be paralyzed or lost regardless of the industry or company size.
Data and Reputation Protection
Loss or leakage of data can severely damage the trust of customers and partners, and a single incident can destroy a reputation built over years.
Business Continuity
Ransomware or DDoS attacks can paralyze system operations and cause significant financial losses, which is why cybersecurity is essential to ensure continuous availability of services.
Compliance with Legal and Regulatory Requirements
Many industries are subject to regulations such as GDPR, the KSC Act, or PCI DSS, and failure to comply can result in heavy fines and penalties.
Protection Against Financial Losses
The cost of an incident is not only system repairs but also lost revenue, compensation, and fines on average, a single data breach can result in losses amounting to millions of euro.
Minimizing the Risk of Human Error
Cybersecurity training reduces the effectiveness of phishing, social engineering, and other manipulation based attacks.
Competitive Advantage
Companies investing in cybersecurity gain a competitive edge, build customer trust, minimize the risk of downtime and losses, and can respond more quickly to threats, maintaining business continuity where others suffer setbacks.
Implementation Process Description
The process of implementing cybersecurity within an organization should be systematic, phased, and aligned with business objectives. Below is a complete structure that works well for most companies from small businesses to large corporations.
Audit
The cybersecurity process includes inventorying assets, identifying threats, assessing security maturity according to standards (e.g., ISO 27001), and determining legal requirements such as GDPR.
Definition of Security Strategy and Policy
Cybersecurity planning involves setting protection objectives, implementing security policies, defining roles and responsibilities, and preparing the budget and action schedule.
Implementation of Technical and Organizational Measures
Cybersecurity encompasses technical solutions (firewalls, MFA, encryption, monitoring) as well as organizational actions (incident procedures, access policies, continuity and recovery plans).
Training and Awareness Raising
Security education includes regular employee training on phishing, social engineering, and password hygiene, exercises simulating attacks, and ongoing internal communication about current threats.
Monitoring and Incident Response
Continuous system monitoring (24/7) by SOC teams or MSSP providers enables rapid anomaly detection, automated alerts, and effective response, reporting, and mitigation of attack impacts.
Audits and Improvement
Regular security audits, penetration tests, and updates to procedures, policies, and technologies allow for continuous improvement of the protection system in line with the PDCA cycle (Plan – Do – Check – Act).
How Can We Help Secure Your Company?
Estimating the costs and scope of a cybersecurity implementation requires a thorough risk analysis, prioritization of business objectives, and consideration of regulatory requirements (GDPR, KSC, ISO 27001). It is essential to determine which assets and infrastructure areas need protection, define the boundaries of implementation (entire organization or selected departments, on-premises or cloud systems), and conduct a detailed assessment of threats and their potential impact. Prioritizing the protection of the most critical elements allows for optimization of both costs and security levels.
Your Needs — Our Solutions
We offer comprehensive cybersecurity support from asset inventory and risk analysis to developing a protection strategy tailored to the client’s specific needs and legal requirements, and implementing effective technical and organizational measures. We help define priorities, prepare action plans, and provide ongoing support in monitoring and improving security, minimizing the risks and costs associated with incidents.
Request a free estimation of your project
We are VAO
Your full-service software development company.
We provide a rock-solid coding you can rely on.
Cybersecurity & NIS2 Compliance
NIS2 Directive, Audits & Threat Protection
We secure software ecosystems, conduct penetration testing, and implement NIS2 compliance frameworks to protect critical IT infrastructure against cyber threats.
Artificial Intelligence for Business
Automation, LLMs & Machine Learning
We integrate custom AI models, Large Language Models (LLMs), and machine learning pipelines into business software to automate workflows and unlock data-driven decisions.
Custom Web Applications
Laravel, Symfony, Drupal & Node.js
We design and build high-performance web systems and B2B platforms. Scalable, secure, and tailor-made software engineered to match your business processes.
Mobile Applications
Flutter, Swift & Kotlin
We develop native and cross-platform mobile apps for iOS and Android. Fast, intuitive digital products that engage users and drive business growth.
Advanced e-Commerce Systems
Magento, Drupal Commerce & Shopify
We build high-performance B2B and B2C e-commerce platforms. From Headless architecture and ERP/CRM integrations to complex multi-store deployments.
Startup MVP Support
From Concept to Production-Ready Product
We transform innovative ideas into scalable market-ready digital products. From UX prototyping to rapid MVP development and post-launch scaling.
IT Consulting & Audits
IT Architecture, Code Review & Consulting
We offer professional tech consulting, code reviews, and software architecture analysis. We identify bottlenecks, eliminate technical debt, and optimize infrastructure costs.
Dedicated Development Teams (Staff Augmentation)
Scale your engineering capacity with top-tier talent
We seamlessly integrate experienced tech experts into your workflows to accelerate delivery, fill skill gaps, and scale your development team reliably.
Legacy Modernization & Code Refactoring
Architecture Upgrades & Technical Debt Reduction
We breathe new life into outdated systems by modernizing legacy architectures, migrating old frameworks, and optimizing performance without downtime.